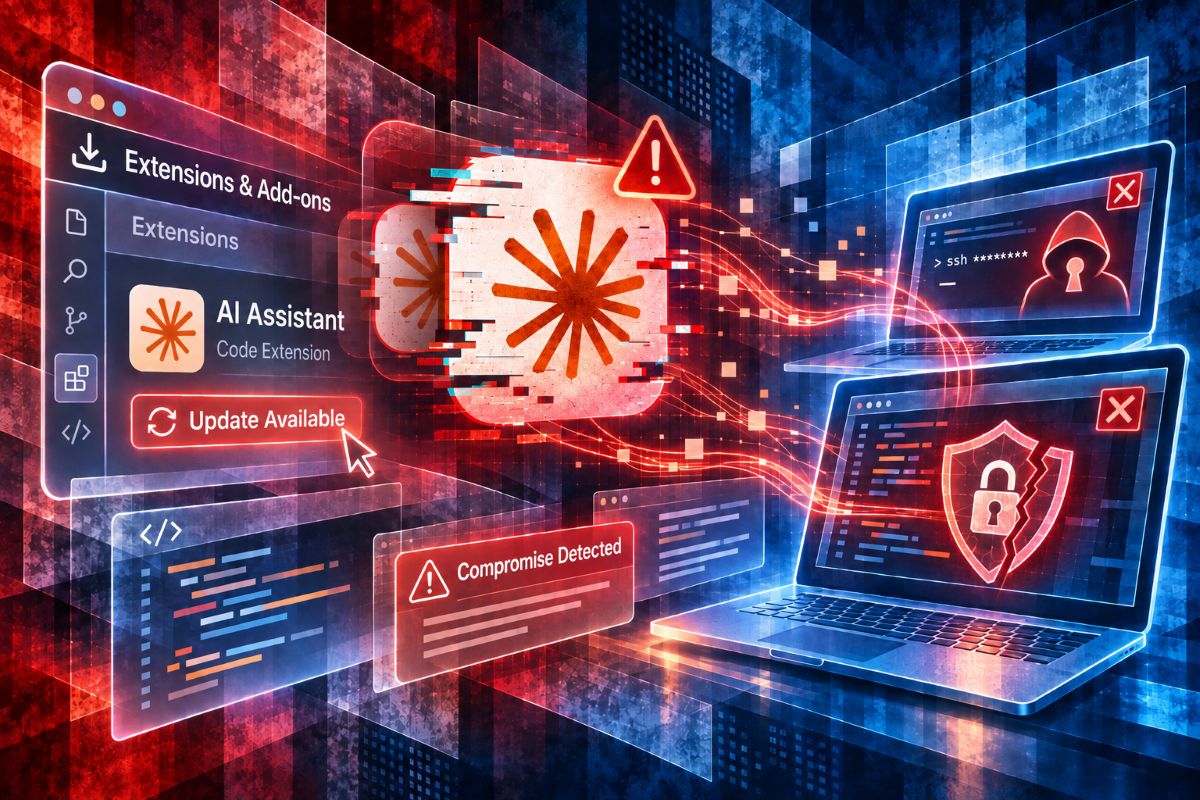

The fake update was available for about 11 hours on Oct. 29, and Cursor said the hacker set up a hidden login on computers that installed it.
Cursor, which makes an AI app for writing software, said a hacker published a fake update to Anthropic’s Claude Code in the store built into Cursor’s app. Cursor said the hacker reached up to 5,000 of its users and set up a hidden login on computers that installed the update.
Developers use Cursor’s store to add tools such as Claude Code to the app, and Cursor can install new versions of those tools automatically. Cursor said the hacker published the fake update under Anthropic’s own name, so it looked like a normal update from Anthropic.
Cursor removed the fake update about 11 hours after it appeared. It then shut down its entire store and checked that the hacker hadn’t changed any other tools. It changed its security keys, rebuilt the store, and brought it back online.
Microsoft, which also offers Claude Code in the store for its own code-writing app, VS Code, examined the fake update and confirmed it never appeared in that store. Anthropic said the hacker did not break into Anthropic itself.
The hacker tried to get remote access to developers’ computers
Cursor said the hacker used the fake update to try to gain remote control of the computers that installed it. Cursor warned that the hacker could then take passwords and other logins stored on those computers.
Microsoft said developers who installed the update ran the hacker’s code as soon as they opened Cursor, without clicking anything. They could keep using Claude Code as normal, with no sign of the attack.
Cursor said the hacker failed to gain control on most Mac and Windows computers because of mistakes in the hacker’s code and because the user would have had to be running Cursor with administrator rights. Cursor did not say how many computers, if any, the hacker gained control of.
Cursor said that even on computers where the hacker failed to gain control, the hacker set up a hidden login. With it, the hacker could get in remotely if the computer’s remote-access setting is ever switched on. The hacker also set the code to restart whenever the computer does and keep trying to reach the hacker’s own computer.
Cursor said the hacker also collected each computer’s name, the user’s name, and the computer’s internet address. Microsoft said the hacker also collected labels showing where passwords might be stored on each computer, but not the passwords themselves.
Cursor and Microsoft tell companies to clean affected computers by hand and delay new updates
Cursor and Microsoft say companies must clean affected computers themselves, because the hacker’s hidden login and code stay on a computer even after the user removes Claude Code. Cursor worked with the company hosting the hacker’s computer to take it offline. Microsoft noted that the hidden login and code remain on affected computers even after the hacker’s computer was taken offline.
Cursor said companies should check any Mac or Windows computer that installed the fake update from its store during those 11 hours, including through automatic updates. Cursor listed the fake update’s version numbers as 2.1.312 and 2.1.313, and published a short check IT teams can run to find the hidden login.
Cursor and Microsoft advise companies to cut affected computers off from company networks, remove the hidden login and code, and consider wiping and reinstalling the computers. Because Cursor cannot rule out that the hacker used the hidden login to take passwords, it advises companies to change any passwords and other logins stored on affected computers.
Microsoft also advised companies whose developers use Cursor to delay automatic updates to tools like Claude Code. That gives the store time to catch and remove a fake update before it reaches company computers.