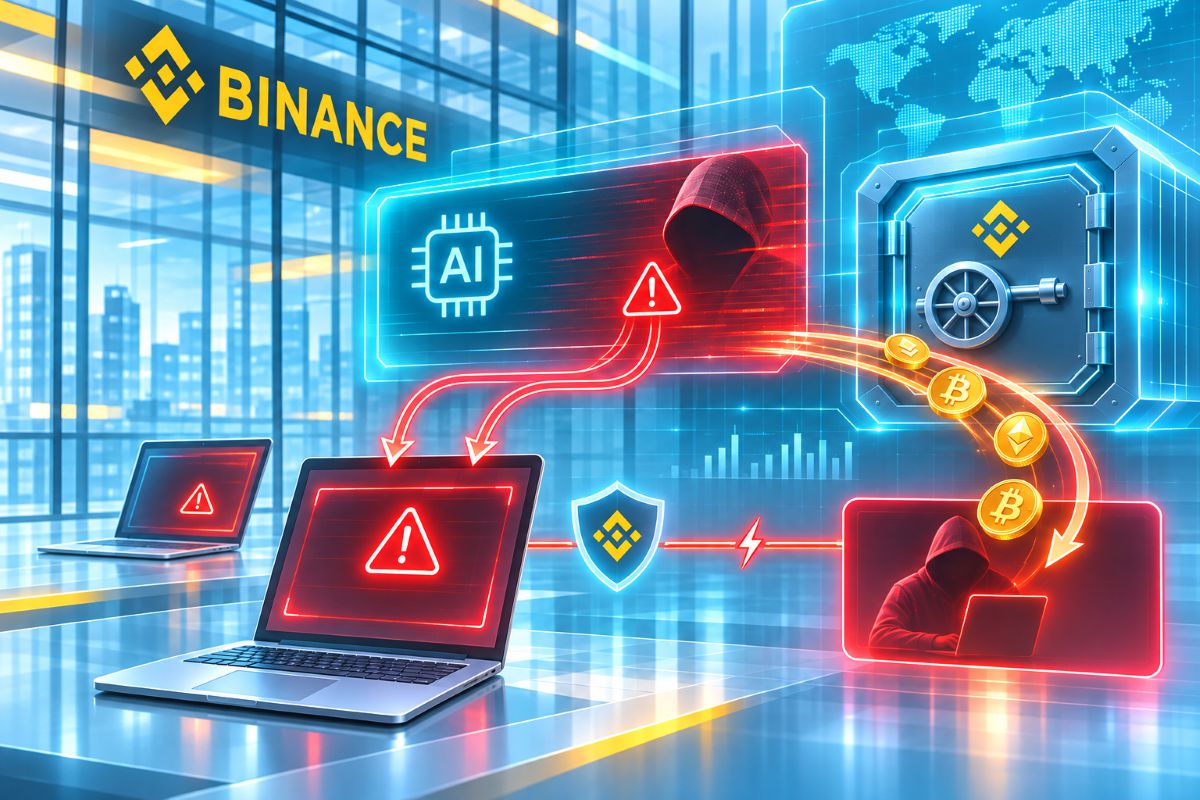

Binance says the attackers broke into one engineer’s computer, then used the company’s internal AI tools to take over two wallet engineers’ computers.
Cryptocurrency exchange Binance said that hackers used its internal AI tools to take over its engineers’ computers before stealing digital assets worth about $6.34 billion. The FBI says North Korea carried out the theft.
Binance says the attackers used its AI tools to take over wallet engineers’ computers
Binance says the attackers first broke into one engineer’s computer in September. On Oct. 20, they used that computer and Binance’s internal AI tools to take control of two more engineers’ computers. Both engineers worked on the systems that run Binance’s wallets. On one of those computers, the attackers found a login with permission to install and run programs on Binance’s servers.
On Oct. 30, the attackers used the other wallet engineer’s computer and that login to reach the service that approves transfers from Binance’s wallets. They then sent the assets to accounts they controlled.
Binance hasn’t named the AI tools or said how the attackers misused them.
Hackers lured Binance engineers with a fake AI coding tool and a fake job
Binance says the attackers started preparing in June. An engineer on its wallet team searched online for a popular AI coding tool. The engineer downloaded a fake installer for it. Binance’s security team spotted the problem, replaced the engineer’s laptop, and changed the engineer’s logins. By then, the attackers had already learned the engineer’s role and who else was on the team.
In September, an attacker posing as a recruiter contacted a second Binance engineer through a legitimate job site. The attackers then held two rounds of fake interviews, one of them by live video. The engineer downloaded a take-home coding test onto a work computer. The test contained malware. Binance says its security tools didn’t catch the malware at the time.
The FBI blames a North Korean hacking group
The FBI said on Oct. 31 that a North Korean hacking group carried out the Binance theft. The FBI blamed the same group for stealing $1.5 billion from the crypto exchange Bybit in February 2025.
TRM Labs, a firm that tracks crypto transfers, called the Binance theft the largest crypto theft on record.
Binance says its users won’t bear the losses
Binance says it will cover the stolen assets from its own reserves. It had replaced 98% of the stolen tokens by Oct. 31. It and its partners have frozen or blocked about $2.85 billion of the stolen assets.
Binance says it has rebuilt the AI tools the attackers used
Binance says it rebuilt the affected AI tools and limited who can use them. It also rebuilt the affected wallet systems, replaced the affected computers, and scanned every employee’s device.
Binance says outside security experts will review the attack and the company’s response. It also plans to set up a security research fund with AI companies.
Attackers targeted AI coding tools and hiring before
On Oct. 29, a hacker put a fake update to Claude Code, Anthropic’s AI coding tool, in the add-on store of Cursor, an AI coding app. The hacker used the fake update to plant a hidden login on users’ computers. The hacker reached as many as 5,000 Cursor users before Cursor removed the update about 11 hours later.
North Korean groups have also used hiring to get inside companies. In June, cybersecurity company CrowdStrike reported that North Korean workers used AI to pass interviews for remote tech jobs at U.S. companies.